How an Online Retailer Stopped Payment Gateway Fraud Before It Scaled
An anonymized walkthrough of how a mid-sized Indian e-commerce business caught a payment gateway exploit attempt early — what worked, and what almost didn't.
💡 In Simple Terms (For Beginners)
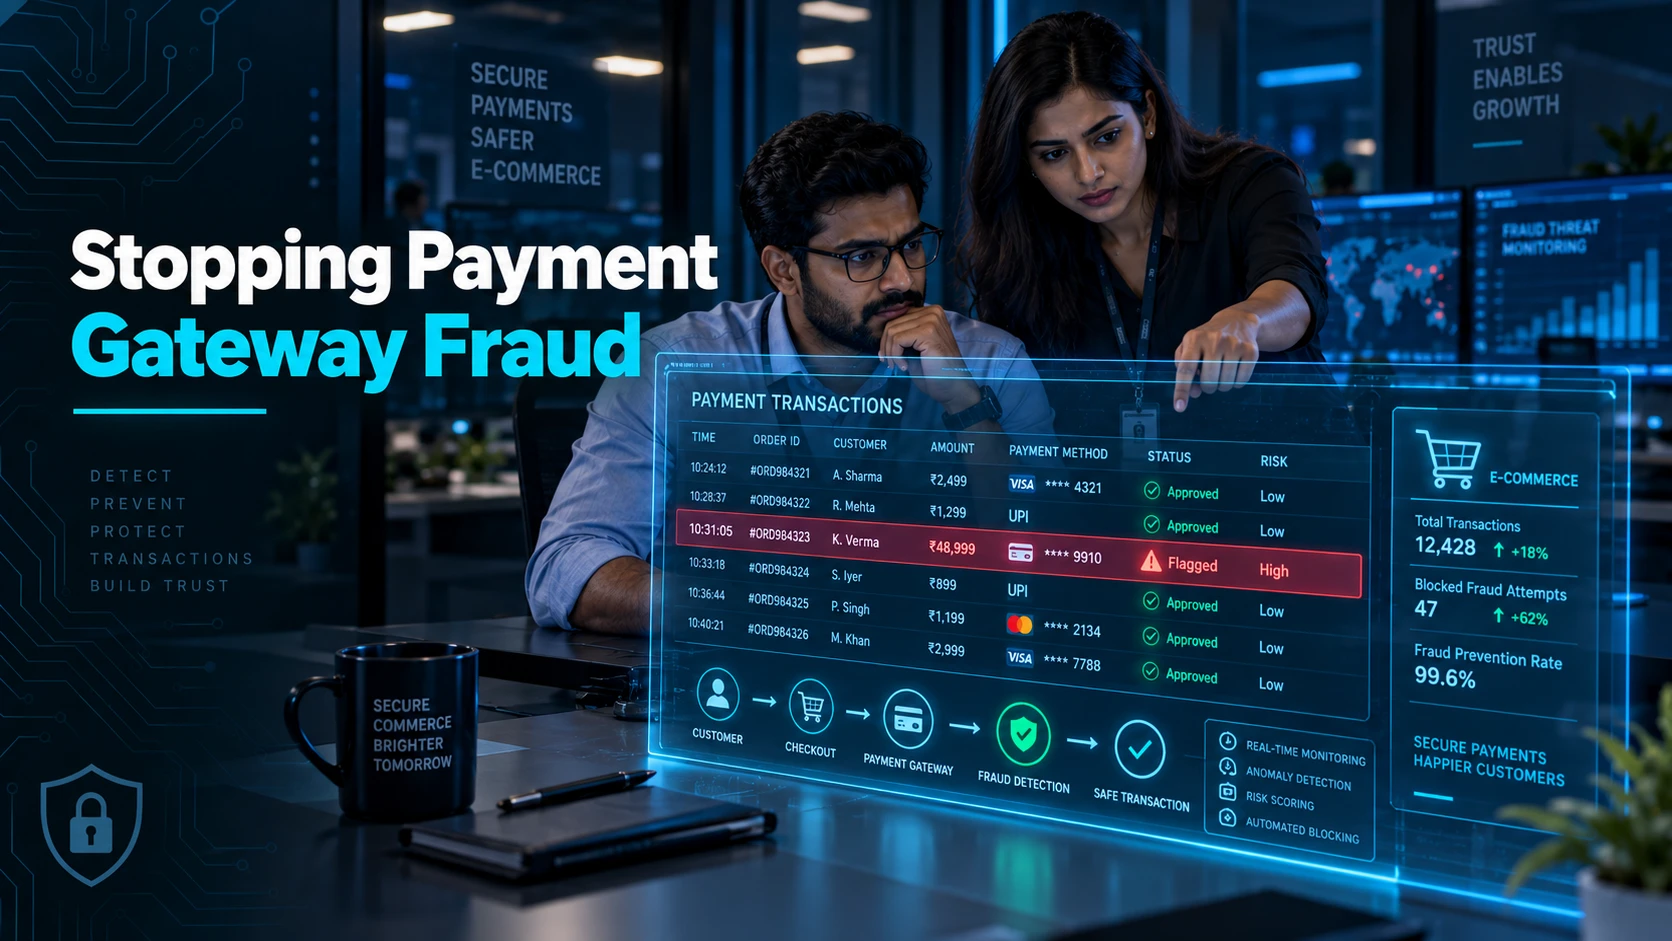
An online store noticed unusual small test transactions on its payment page — a common early sign that someone is probing for a way to commit larger fraud later. Catching that pattern early stopped a bigger problem.
- Small, repeated test transactions on a payment page are often reconnaissance for a larger fraud attempt, not isolated glitches.
- Transaction monitoring caught the pattern before it scaled into real financial loss.
- The fix combined a technical control (rate limiting) with a process one (finance team alerting).
CASE STUDY · September 6, 2026 · 7 min read · By Hardik Patel
This is an anonymized, illustrative account based on patterns we see across e-commerce client engagements — not a single identifiable company. A mid-sized Indian online retailer noticed a cluster of small, failed transactions hitting its payment gateway from a narrow range of IP addresses over a short window — an early pattern worth recognizing before it becomes a larger fraud incident.
The Early Warning Sign
A burst of small-value transaction attempts, many declined, concentrated in a short time window and originating from a narrow set of sources, is a common precursor to card-testing fraud — where a fraudster uses small transactions to validate stolen card numbers before attempting a larger purchase.
In this case, the pattern surfaced in the payment gateway's own dashboard, but nobody on the team was actively monitoring it as a security signal — it initially looked like routine failed-payment noise rather than a targeted probe.
How It Was Actually Caught
A routine VAPT engagement included a review of payment flow logs as part of assessing the checkout process, and the unusual transaction-attempt pattern stood out immediately to someone looking specifically for anomalies rather than day-to-day operational noise.
This illustrates a recurring theme across client engagements: the data needed to catch an attack early often already exists in a dashboard somewhere — the gap is usually that nobody is looking at it with a security lens, not that the data is missing.
The Fix: Technical and Process
The response combined a technical control — rate-limiting transaction attempts per card/IP combination within a short window — with a process control: routing an alert to the finance team whenever that rate limit triggers, so a human reviews the pattern rather than the system silently blocking and moving on.
Neither control alone would have been sufficient — the technical limit stops the immediate probing, but the human alert is what catches a genuinely novel pattern the automated rule wasn't specifically built to recognize.
Key Takeaways
- Small, clustered failed transactions are a recognizable card-testing fraud pattern, not routine noise.
- The relevant data often already exists in a payment dashboard — the gap is usually attention, not missing data.
- Combining a technical rate-limit with a human alert catches more than either control alone.
Frequently Asked Questions
Q: What is card-testing fraud?
A: A pattern where a fraudster runs small transactions against stolen card numbers to check which ones are still valid, before attempting a larger fraudulent purchase with the confirmed-valid cards.
Q: How can a business tell the difference between normal failed payments and a fraud pattern?
A: A cluster concentrated in a short time window, from a narrow range of sources, with small transaction values, is the pattern worth investigating — isolated, spread-out failures are more likely routine.
How iTechFixr Can Help
Our VAPT audits for e-commerce clients specifically include a review of payment flow logs and transaction patterns, not just the application code itself.
Need Help With This?
Talk to Hardik directly about your organisation's cybersecurity needs — get a tailored response within 24 hours.