CEH Career Roadmap in India: From Zero to Your First Security Role
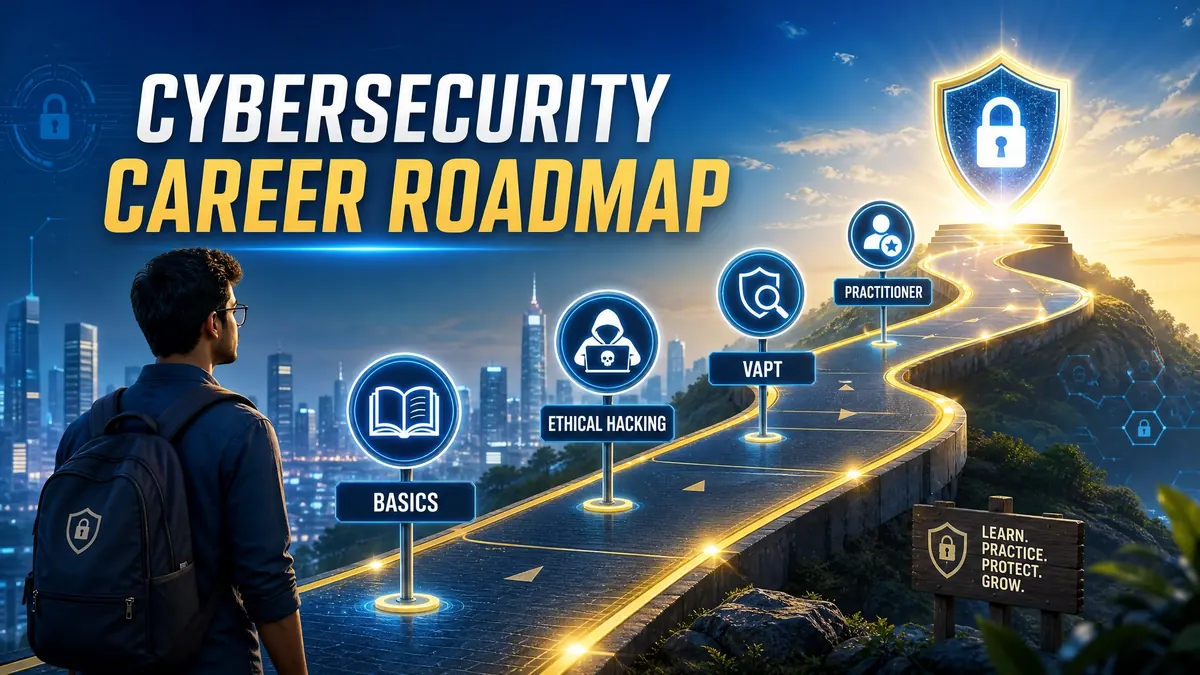
CEH is a good credential for someone who already understands networks and can already break a practice machine. It is a poor starting point for someone who has never opened a terminal. Here is the order we would follow, and where the certificate actually helps.
💡 In Simple Terms (For Beginners)
CEH is a good credential for someone who already understands networks and can already break a practice machine. It is a poor starting point for someone who has never opened a terminal. Here is the order we would follow, and where the certificate actually helps.
- Build networking, Linux and basic web knowledge first. Certificates come after that, not before.
- Practise on legal labs every week. Employers ask what you have done, not only what you have passed.
- CEH is one step on the path. It works best as proof of breadth, alongside hands-on evidence.
- Plan in months, not weeks. Twelve to eighteen months from a standing start is a fair planning figure.
ETHICAL HACKING · September 30, 2026 · 7 min read · By Hardik Patel
Start with the skills, not the certificate
Most people who struggle with CEH are not weak at exam technique. They are missing the layer underneath it. The exam and the syllabus assume you already know how a network behaves, so learn that first.
Work through these in roughly this order:
- Networking basics. IP addressing, subnets, DNS, DHCP, TCP versus UDP, ports, and what a firewall actually filters. If you cannot explain what happens when you type a website address into a browser, stop here and fix that.
- Linux command line. Files, permissions, processes, package installs, and reading logs. Most security tools run on Linux, and Kali Linux is the usual starting point.
- Windows basics. Users, services, the registry, event logs. Most Indian offices run Windows, so most of what you test will too.
- Web basics. HTTP requests and responses, cookies, sessions, forms. Then the common web flaws listed in the OWASP Top 10.
- A scripting language. Python is enough. You do not need to be a developer. You need to read a script and change a few lines.
Only after that does the CEH syllabus start to feel like organised revision instead of a wall of new words. The phases it teaches (reconnaissance, scanning, enumeration, gaining access, maintaining access, covering tracks) map directly to what you will do in labs.
Where to practise, legally
Reading about an attack and running it against a target are different skills. Use only systems you own or that are built for this purpose. Testing anyone else's system without written permission is an offence under the IT Act, 2000.
- Your own home lab. VirtualBox or VMware on a laptop, one Kali Linux machine, and one or two deliberately vulnerable machines such as Metasploitable or DVWA (Damn Vulnerable Web Application). This costs nothing but disk space.
- OWASP Juice Shop. An intentionally insecure web app with guided challenges.
- TryHackMe and Hack The Box. Browser-based labs with structured learning paths. Both have free tiers and paid tiers; check their sites for current plans.
- VulnHub. Downloadable vulnerable machines you run offline.
- Capture the Flag (CTF) events. Many Indian colleges and communities run them. They teach you to work under time pressure and with teammates.
Keep a simple write-up habit. After each lab, write half a page: what you scanned, what you found, what worked, what did not. Ten good write-ups on a public page or a GitHub repository tell an interviewer more than a certificate line does. Our guide to learning ethical hacking online through practical labs covers how to build the lab and what to ask a course.
Where CEH fits
CEH (Certified Ethical Hacker) is issued by EC-Council. It covers a wide range of attack techniques and tools at an introductory to intermediate level. It is a breadth certificate: it shows you have seen the whole map. EC-Council also offers a separate practical exam for CEH, which tests hands-on skill. Check EC-Council's website for the current exam format and eligibility rules before you plan around them.
How to think about it:
- Good for: proving familiarity with the vocabulary and techniques, satisfying a job listing that names it, and giving structure to your study.
- Not enough on its own for: a penetration testing role. Testers are hired on demonstrated hands-on ability.
- Sits alongside: CompTIA Security+ for foundations, eJPT for a beginner hands-on test, and later OSCP for deep offensive skill. You do not need all of them. Pick the one that matches the job you want.
If you are aiming at a defensive role such as a SOC analyst, spend as much time on log analysis and incident handling as on attack tools.
Entry roles you can realistically target
Very few people start as a penetration tester. These are the usual first doors:
- IT support or system administration with security duties. You learn how real offices are built and broken.
- SOC analyst (Level 1). You watch alerts, triage them and escalate. Log reading and clear writing matter more than exploit skills.
- Junior VAPT (vulnerability assessment and penetration testing) analyst. You run scans, verify findings and write reports, under a senior tester.
- GRC (governance, risk and compliance) support. You help with audits, policies and evidence for frameworks such as ISO 27001 and India's DPDP Act. Non-technical strengths count here.
- Security awareness or training assistant. Useful if you like explaining things to people.
Job requirements vary widely by employer and city. Read ten current listings for the role you want and note the tools and skills they repeat. That list is your syllabus.
A realistic timeline
This is a planning estimate, not a survey result. It assumes about 8 to 10 hours of study and lab time each week.
| Stage | Roughly | What you have at the end |
|---|---|---|
| Networking, Linux, Windows, web basics | Months 1 to 4 | Comfort in a terminal, a working home lab |
| Guided labs and first write-ups | Months 4 to 8 | Ten or more written-up labs, a few CTFs |
| CEH preparation and exam | Months 8 to 12 | Certificate, wider tool knowledge |
| Applications, interviews, a portfolio | Months 10 to 18 | A first role or an internship |
If you already work in IT support or networking, the first stage can shrink by a few months. If you are studying full time, it can compress, but hands-on hours still cannot be skipped.
Key takeaways
- Foundations first: networking, Linux, Windows and web basics decide how quickly the rest goes.
- Practise only in legal labs and write up what you learn.
- CEH shows breadth. Hands-on evidence shows ability. Employers look for both.
- Most first roles are analyst, support or junior VAPT positions, not senior tester jobs.
- Plan in months. Twelve to eighteen is a fair figure from a standing start.
Frequently asked questions
Q: Can I take CEH straight after Class 12 or a non-IT degree?
A: You can study for it, but eligibility is set by EC-Council, so check their current rules. Practically, you will do better by spending a few months on networking and Linux before touching the syllabus.
Q: Is CEH enough to get a job in cybersecurity in India?
A: Rarely on its own. It helps a listing that names it, but interviewers usually test practical skills. Pair it with lab write-ups and, if possible, an internship or a support role where you handle real systems.
Q: Is programming required?
A: Not deep programming. You should be able to read Python or Bash, run a script and adjust it. Web testing is easier if you also understand basic HTML and JavaScript.
Q: Which is better for a beginner, CEH or CompTIA Security+?
A: Security+ is broader on defence and fundamentals. CEH is centred on attacker techniques. Beginners often start with the fundamentals and add CEH when they want the offensive view. Choose by the job you are targeting.
Q: Is ethical hacking legal in India?
A: Testing systems you own, or where you hold written permission from the owner, is legal. Testing anyone else's systems without permission can be an offence under the IT Act, 2000, however good your intentions.
How iTechFixr can help
iTechFixr Infotech LLP runs cybersecurity training in Pimpri-Chinchwad, Pune, led by Hardik Patel, a CEH v12 holder. We train organisations only: colleges, universities and companies, in groups of at least 15. Our CEH v13 AI course is 42 hours of live training, 70% practical, delivered online or at your site. The EC-Council exam is separate, and we do not promise job placement. If you are a TPO, HOD, or in HR or L&D, see our training programs and talk to us about a batch for your students or staff.
Need Help With This?
Talk to Hardik directly about your organisation's cybersecurity needs — get a tailored response within 24 hours.